
About Joey Victorino
The person you meet does the work.
I am Joey Victorino. I run a one-person consulting practice across security testing, incident investigations, lawful research, negotiation, and AI security reviews.
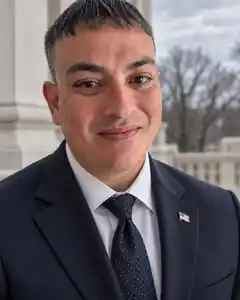
Independent consultant
Why one person?
You work directly with me from the first discussion through the final deliverable. I perform the work myself, with no junior handoff and no large-firm staffing structure. If your matter needs a larger team or a specialist outside my scope, I say so before accepting it.
Work you can inspect
You can read my security writing and inspect public code published under my name. A repository or sample shows work you can examine; it does not establish a client outcome, an employer endorsement, or a guarantee about your systems.
Insurance
Before signing, request written confirmation of any professional liability and cyber errors and omissions coverage, limits, and exclusions relevant to your engagement. We agree your insurance requirements before I accept the work.
Conflicts and incentives
I disclose relevant financial interests, affiliations, and fee incentives before accepting work. If a conflict prevents me from giving you an independent conclusion, I decline the engagement.
What I don't do
Limits you can rely on.
- I do not access systems, accounts, buildings, or records without the required authority and permission.
- I do not offer covert collection, unlawful pretexting, harassment, or personal surveillance. I decline research that lacks a legitimate, agreed purpose.
- I do not provide legal advice, practice medicine, clear medical devices, or promise that a review establishes regulatory compliance.
- I do not guarantee recovery, ransom savings, a particular research finding, or the discovery of every security weakness.
- I do not provide a continuously staffed, round-the-clock response center or delegate your engagement to junior staff.
A place to start
One hour. One decision.
Work through your problem before committing to a larger engagement.